Anthropic's expanded Cyber Verification Program offers three access tiers for security work, with eligibility and data-retention conditions.
The October 6, 2026 announcement distinguishes Defense, Red Team and Specialized access. The aim is to let qualifying professionals perform work that more conservative cyber safeguards may block. Applying for access is a supplier decision; permission to test a system is a separate responsibility.
For a manager buying security services, the significant change is who can obtain advanced capabilities under which controls. A program badge does not establish that an engagement has the right scope, handles sensitive data appropriately or produces reliable findings.
Match access to the authorized work
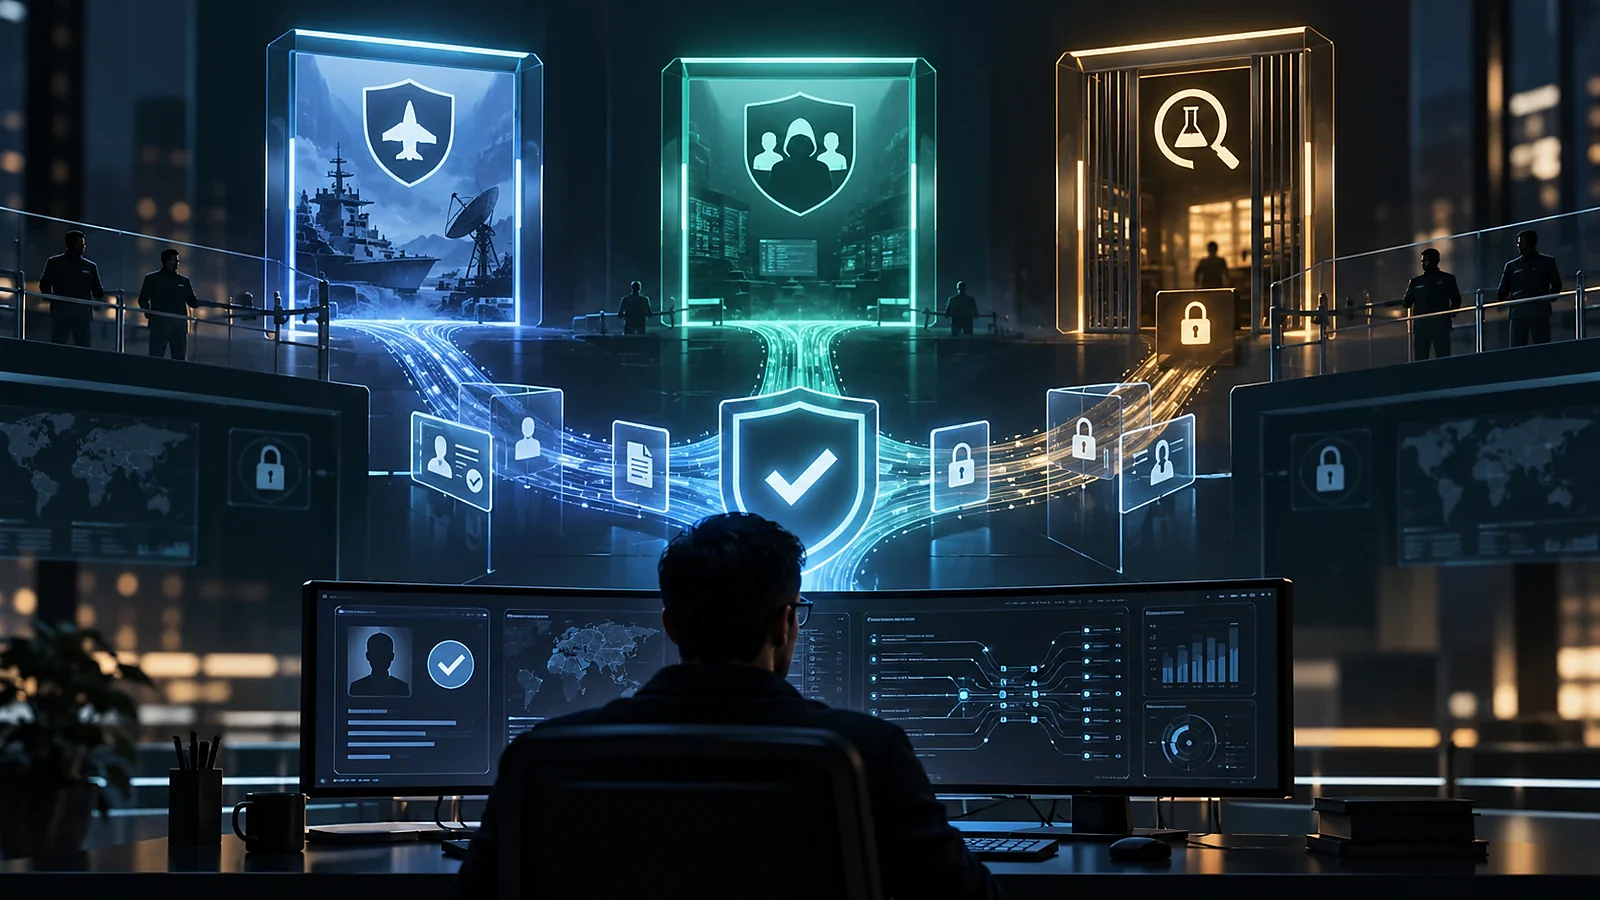
Anthropic describes Defense Access for defensive tasks and allows applications from qualifying organizations, maintainers and researchers. Red Team Access adds authorized adversarial testing and is currently for organizations rather than individual researchers. Specialized Access is restricted to a smaller group testing consequential safety systems.
Those categories are supplier descriptions, not a reason to give a contractor unrestricted authority. Define the systems in scope, permitted actions, excluded actions, contact for unexpected effects and stopping conditions in the engagement itself. The model's permission level cannot replace the system owner's authorization.
An individual researcher should also avoid assuming that approval in one tier makes every use available. Ask which approved access applies to the specific model, account and platform. The current program help says Anthropic may narrow or withdraw a grant and that its usage policy continues to apply.
For smaller organizations, wider eligibility could bring useful tools within reach. The operational advantage still depends on having people who can interpret findings, prioritize fixes and avoid disrupting the systems they are protecting.
Retention belongs in the decision before the upload
The current help documentation says the program requires retention to monitor misuse, while recognizing specified zero-retention exemptions for organizations with qualifying existing access. It also describes Enterprise Frontier Safeguards as forthcoming. Do not treat the proposed customer-controlled storage option as already available on the strength of that language.
Before sending code, logs or vulnerability details, confirm the retention terms for your organization and delivery channel. Determine what information is necessary for the task and what can be omitted. A security workflow may involve details that would be especially damaging if exposed elsewhere.
That creates a legitimate tradeoff. Monitoring may help a supplier identify abuse, while customers may want tight control over sensitive material. An organization should assess the actual terms rather than assuming that “enterprise” means zero retention or that every exemption applies to it.
Access approval is not independent safety evidence
Anthropic reports its own tests of the tiers. Those results describe particular evaluated scenarios and configurations. They do not establish that misuse is impossible or that every legitimate task will work without unnecessary blocking.
WIRED's July reporting covered earlier incidents involving real systems during evaluations. It supplies context for why containment and oversight matter. It does not evaluate the October program or prove that its safeguards fail.
Anthropic benefits from expanding security adoption while retaining control over access. Defenders may gain more capable assistance. System owners and people affected by an engagement could bear the cost of an overbroad test, even if the user is a legitimate professional. Verified identity is useful; it cannot settle every question about intent, scope and execution.
Watch independent evaluations, documented changes to retention options and reports of both prevented misuse and wrongly blocked legitimate work. For an employer considering the program now, begin with a bounded task and review the outputs with qualified staff before expanding authority.
Frequently Asked Questions
Can individual researchers apply?
Anthropic includes qualifying individual researchers in Defense Access. Its announcement says Red Team Access is currently limited to organizations.
Does program approval authorize testing someone else's systems?
No. The announcement limits red-team activity to systems the organization is authorized to test. Establish that authorization separately.
Does every participant receive zero data retention?
No. Current documentation requires retention, with specified exemptions. Confirm the terms for your organization and channel before submitting sensitive material.
Is Enterprise Frontier Safeguards available already?
The reviewed sources describe it as forthcoming. This article does not establish a completed launch or eligibility for a particular customer.
Do Anthropic's benchmark results prove the program is safe?
No. They are company-run evaluations with a defined scope. Independent evidence and your own controlled assessment remain relevant.